Resources
The ProbeIQ blog
Field notes on attack surface management, continuous scanning, and reporting that people actually read.
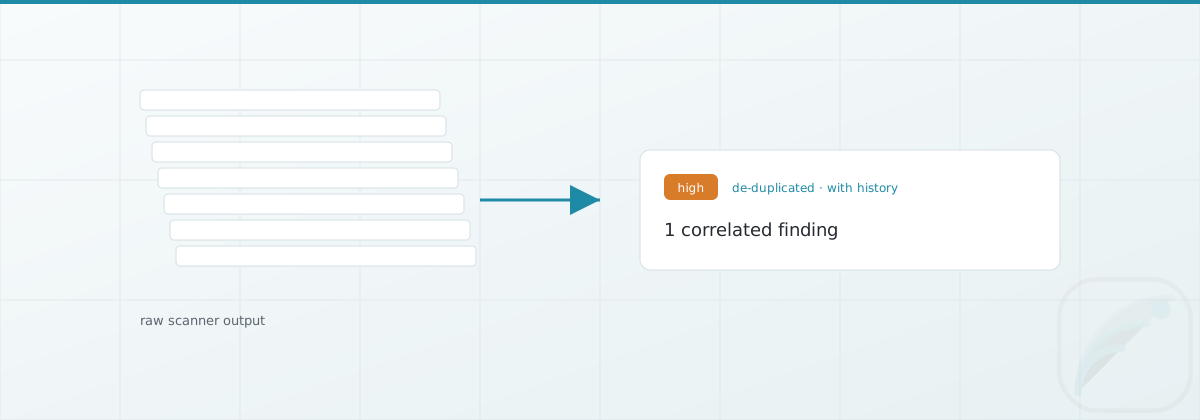
ASM vs. a pile of scanner output: why correlation is the product
Running Nuclei, naabu and httpx on a cron isn't attack surface management. The value isn't the scan — it's what happens to the output afterward.
Read →
The edge keeps breaking: why perimeter CVEs outrun your pentest cadence
VPNs, firewalls, and file-transfer appliances are the devices attackers hit first — and they've been breaking on a monthly cadence. An annual pentest can't keep up. Continuous awareness can.
Read →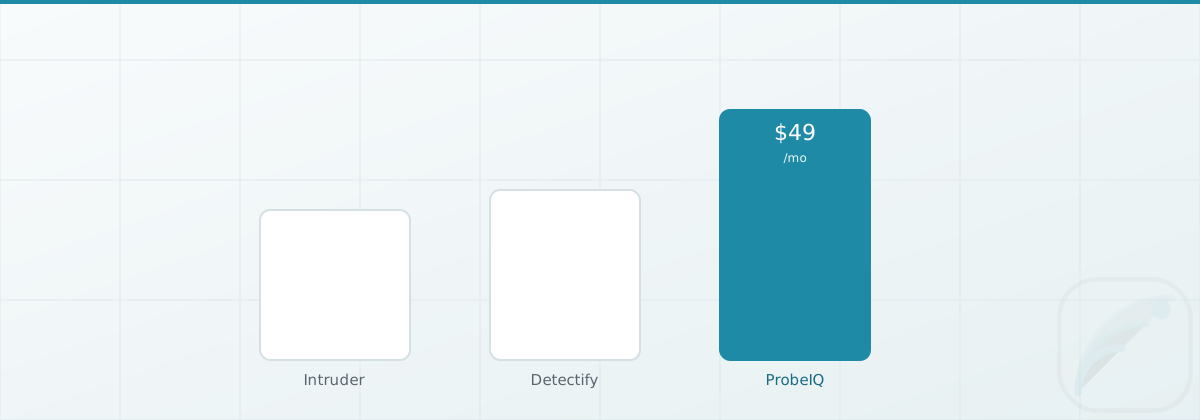
Intruder vs. Detectify vs. ProbeIQ: an honest comparison for mid-market teams
Three continuous external-security tools, three different bets. A fair look at where each fits — including where the other two are genuinely strong.
Read →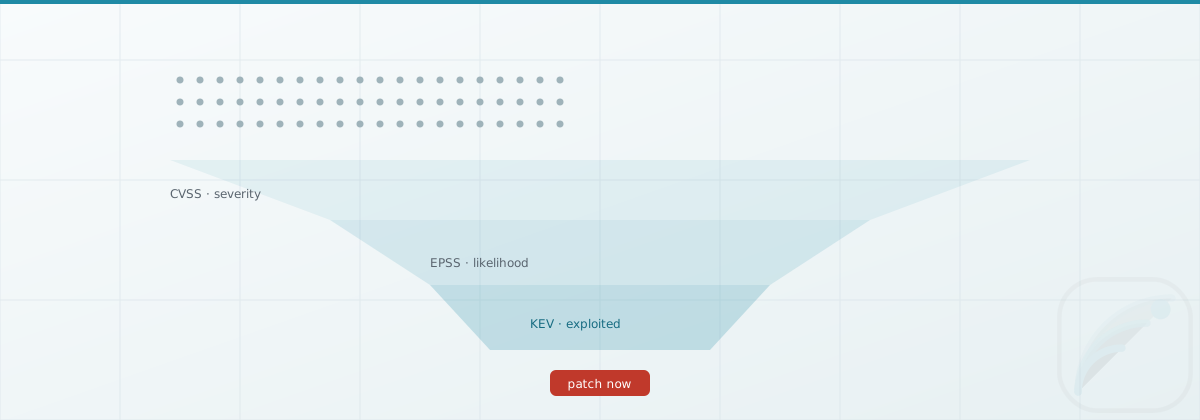
Beyond CVSS: prioritizing exposures with EPSS and CISA KEV
Only about 5% of CVEs are ever exploited, and the NVD can no longer enrich them all. Patching by CVSS score alone is a losing game — here's the risk-based way.
Read →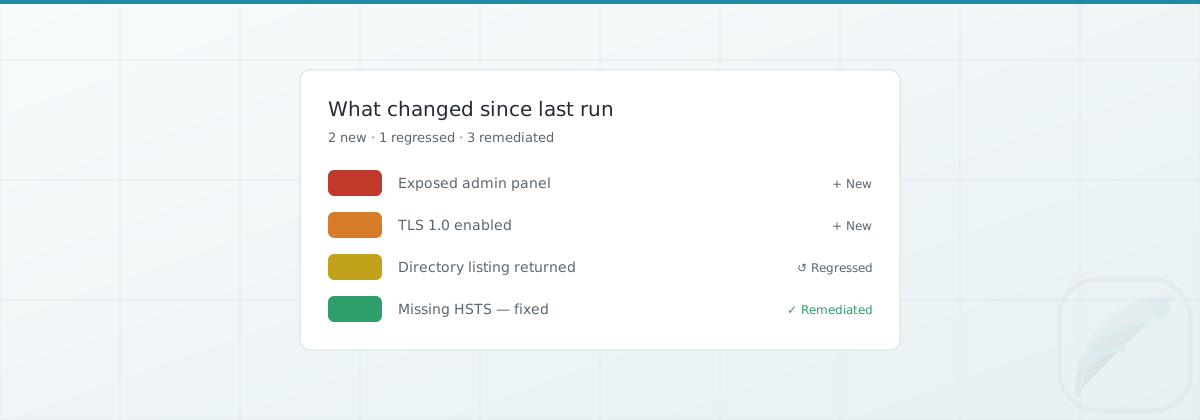
"What changed since last run" — the security report your execs will actually read
Continuous scanning produces a firehose. The signal is the delta — new, regressed, remediated, newly-discovered. That diff is the report people open every week.
Read →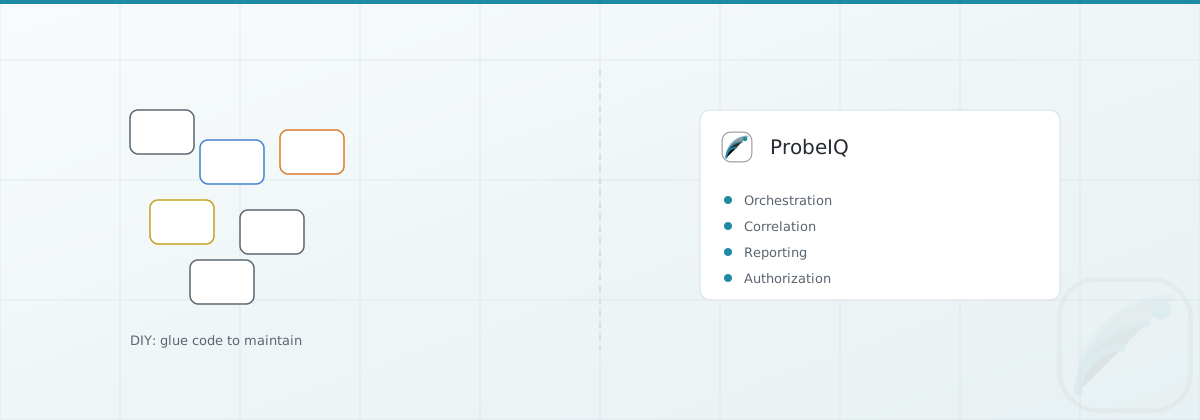
Build vs. buy: when stitching open-source scanners together stops scaling
DIY ASM with open-source tools is the right first move. Here's the honest accounting of where it starts to cost more than it saves — and when it doesn't.
Read →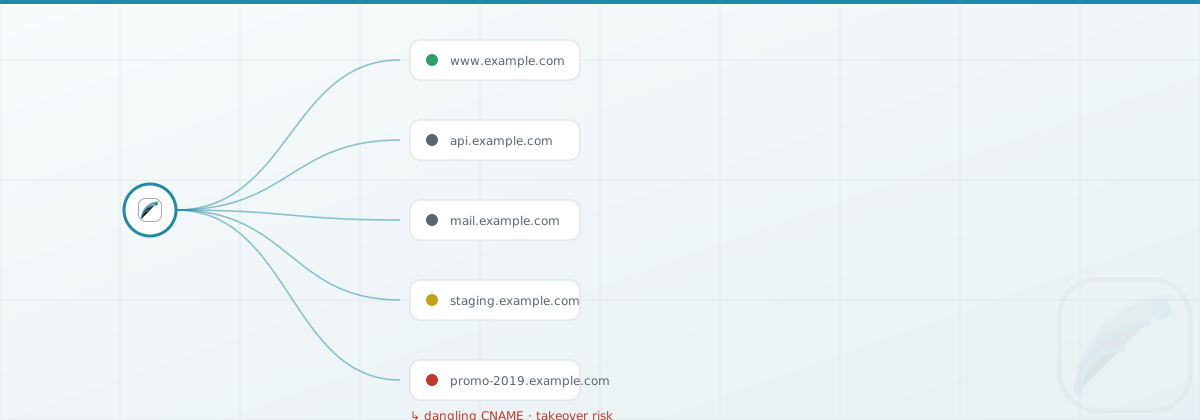
From subdomain enumeration to takeover detection: a practical 2026 workflow
The assets most likely to hurt you are the ones you forgot about. Here's a repeatable pipeline — passive discovery through dangling-record takeover detection.
Read →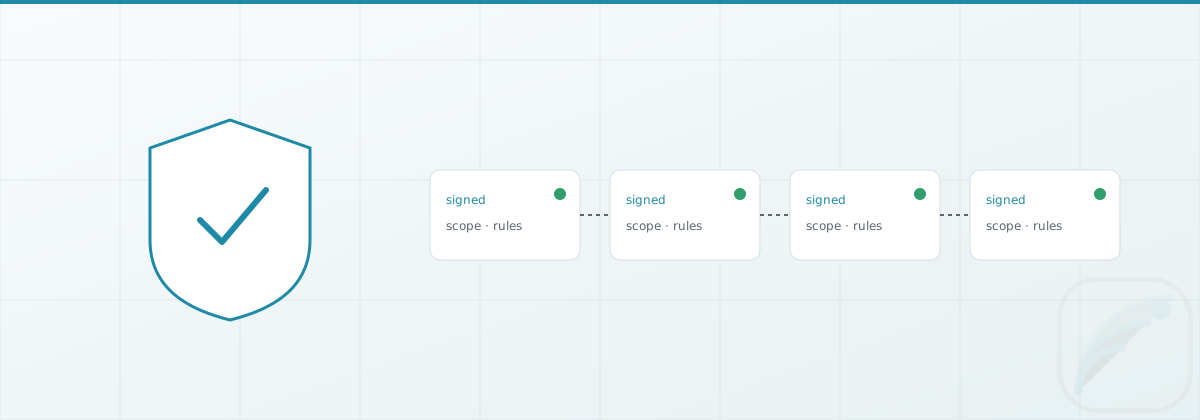
The defensible scan: why authorization is a feature, not paperwork
A scanner that will point anywhere is a liability. ProbeIQ can only touch assets you've proven you own and signed off to test — enforced at every layer and recorded in a tamper-evident log.
Read →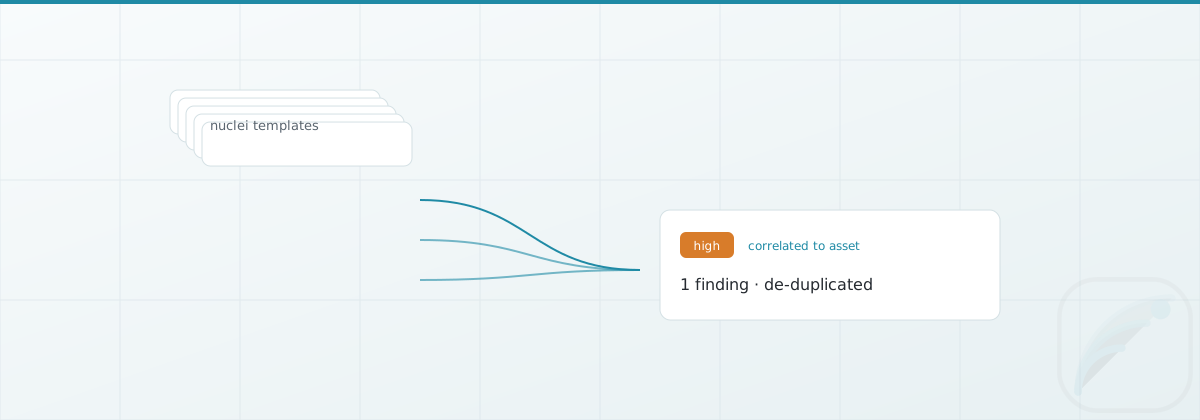
Running Nuclei at scale: correlation, de-duplication, and taming false positives
Nuclei is a superb engine. Pointed at a real, growing attack surface every day, it's also a firehose. Here's what it takes to operationalize it.
Read →
External Attack Surface Management, explained: continuous monitoring vs. the annual pentest
What ASM actually is, why your internet-facing footprint drifts faster than a yearly pentest can keep up with, and the pieces a real ASM program needs.
Read →
Introducing ProbeIQ: continuous attack-surface monitoring without the enterprise tax
Mid-market teams and agencies are stuck between annual pentests, a pile of DIY scanner scripts, and ASM platforms priced for the Fortune 500. ProbeIQ is the middle path.
Read →